FBI warns ARTEX AI tool cuts cyberattacks to under three hours
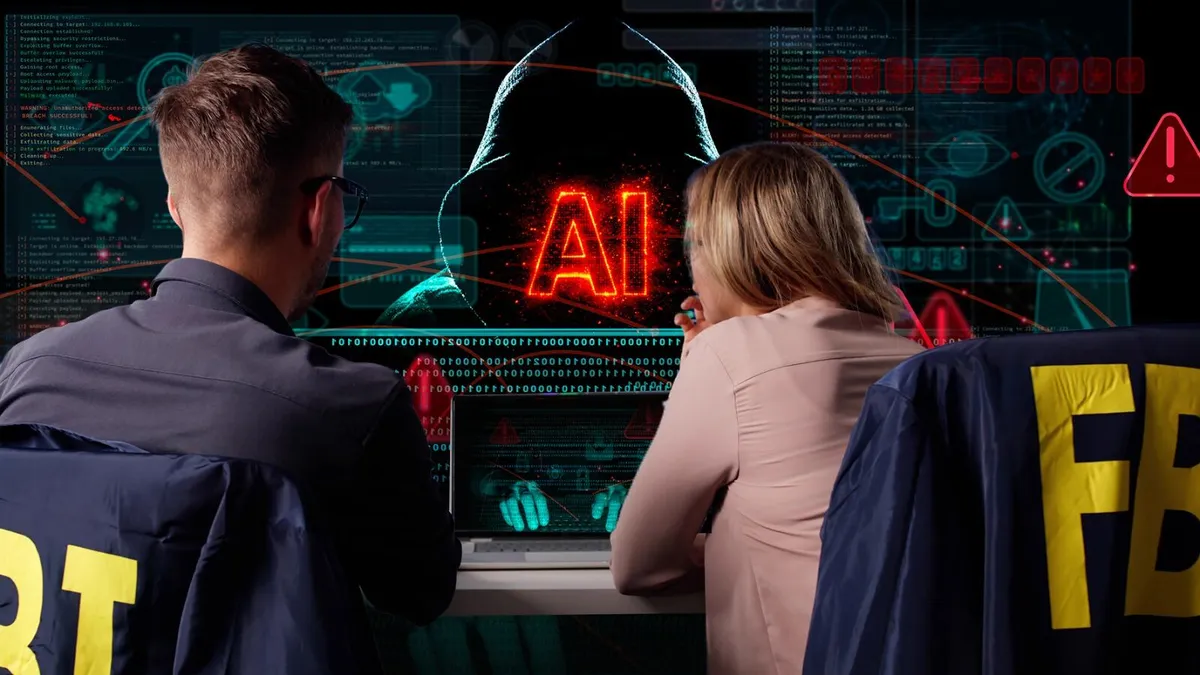
The FBI issued a flash advisory on ARTEX, an open-source AI penetration-testing framework used by cybercriminals and state-aligned hackers to automate intrusions worldwide.
KEY POINTS
- ARTEX is an open-source AI penetration-testing framework written in Go
- It can cut intrusion time from initial targeting to privileged access to under three hours
- The tool automates reconnaissance, exploitation, credential theft, and data extraction
- It was linked to the October ConnectWise supply-chain compromise affecting over 2,250 tenants
- The FBI urges organizations to strengthen access controls and report compromises
The FBI has warned that artificial intelligence tools are making cyberattacks faster and easier to carry out. The agency specifically flagged ARTEX, an open-source penetration-testing framework written in the Go programming language that uses large language models to automate security-related tasks.
According to an FBI document published on November 13, 2026, ARTEX can reduce the time needed to move from initial target selection to privileged system access to under three hours. The tool automates network reconnaissance, vulnerability identification, system exploitation, credential theft, and data extraction using specialized AI agents.
The FBI said ARTEX allows complex operations against multiple targets simultaneously and requires minimal human intervention once natural-language instructions are converted into automatic commands. The agency noted that the technology lowers the technical skills needed to conduct such attacks.
The warning also referenced the October ConnectWise supply-chain compromise, which exposed Microsoft 365 customer environments and involved attempted authentication against more than 2,250 downstream tenants. The FBI urged businesses to strengthen access controls, monitor suspicious automated activity, and report potential compromises.
The advisory was issued by FBI Dallas on November 17, 2026, while El Comercio reported the alert on November 18, 2026. One outlet said the warning was published the previous week, while the other tied it to the November 13 IC3 document.
2 more sources below
COMMENTS (0)
No comments yet. Be the first.
RELATED STORIES
Spanish judge opens criminal probe into Julio Iglesias over sexual assault claims
Audiencia Nacional judge Antonio Piña admits a partial complaint by two former employees, scheduling their testimony for February 3.
GTA 6 launches November 19 with rolling midnight release on PS5 and Xbox Series X|S
Rockstar Games releases Grand Theft Auto VI at local midnight in each region, starting with New Zealand on November 19, 2026.
Security forces kill LeT commander Lateef Bhat in Kulgam mosque operation
Lateef Bhat, described as Lashkar-e-Taiba's last known active local terrorist in Kashmir, was killed after refusing surrender appeals during an early-morning encounter in Zangalpora village.
- HGS toll penalties multiply debts across Turkey, drivers complain
- Eurogroup President Says Greece Can Lead in Artificial Intelligence
- GTA VI launches worldwide amid Asia restrictions and record sales forecasts
- Mexico City Authorities Forecast Multiple Protests Across Mid-November
- Mitsotakis visits Cyprus for fourth intergovernmental summit
This page was compiled with AI assistance from the outlets named above and passed an automated language check before publication. Montegre has no reporters of its own; the byline names the outlets the story was compiled from. Method and editorial standards