Google Reports First Fully Automated AI Cyberattack, Exploit Agent Found on Exposed Server
Google says attackers used AI to find and exploit software flaws without human involvement for the first time.
KEY POINTS
- Google announced fully automated AI cyberattacks on November 16, 2026
- The exploit_agent tool found and exploited software flaws without human involvement
- The system operated from an exposed staging server and used multiple AI models
- Some configuration files contained Russian-language instructions and comments
- Google said the clues do not establish a specific operator
Google said on November 16, 2026, that fully automated AI cyberattacks have begun. Its Google Threat Intelligence Group, working with the Mandiant incident response team, reported that attackers used AI to automate vulnerability discovery and exploitation without a human in the loop.
The discovery centered on a tool called exploit_agent found on an exposed staging server. The server acted as an unlocked workshop where attackers prepared their operations. Google did not name the commercial or locally run AI models that powered the system.
“fully automate vulnerability discovery and exploitation without a human in the loop for the first time”
The tool watched popular web software for security updates. When companies release patches, old and new code versions become public. The AI compared the versions to locate flaws, then wrote exploit code to take advantage of them.
It attacked websites that had not yet installed the fixes. Afterward, it ran follow-up scripts on its own. The server also contained stolen victim data and tools for scouting hacked systems, guessing passwords by brute force, and installing webshells.
Some configuration files included instructions and comments written in Russian. One file referred to API keys for language models in an exploit_agent pilot project. Google said these clues suggest a Russian-speaking environment but are not enough to identify an operator.
Google described the event as the first time criminals fully automated software vulnerability research and exploitation through AI agents. The company did not name the victims or say how many systems were affected.
2 more sources below
COMMENTS (0)
No comments yet. Be the first.
RELATED STORIES
IEA says Iran war energy shock will permanently reshape global power systems
The International Energy Agency warns the world cannot return to pre-crisis energy patterns after the Iran war disrupted global markets.
India revises PUC certificate validity rules for vehicle categories
New rules tie pollution certificate validity to emission standard, vehicle age and transport use.
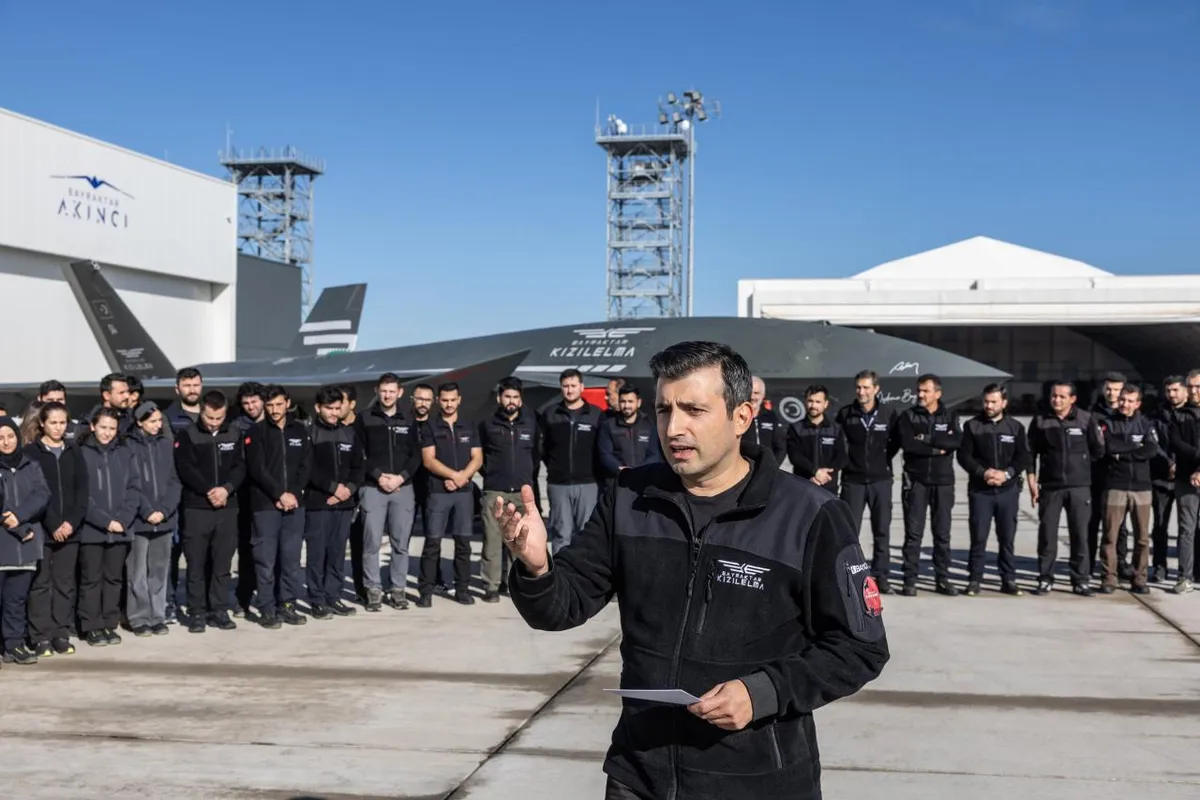
Turkey receives first Kizilelma combat drone, a world first
Turkey becomes the first country to induct an unmanned combat aircraft into its armed forces.
- Denmark and Greenland approve expanded U.S. military bases in Arctic security deal
- Anthropic Founders Set to Become Billionaires in Record Nasdaq IPO
- Milan court postpones final hearing in child social media lawsuit against Meta and TikTok until January 21
- European Commission Hit by Cyberattack, Staff Data at Risk
- Mother seeks lessons at inquest for slain Irish UN peacekeeper Sean Rooney
This page was compiled with AI assistance from the outlets named above and passed an automated language check before publication. Montegre has no reporters of its own; the byline names the outlets the story was compiled from. Method and editorial standards