DarkSword iPhone Hack Steals Crypto Seed Phrases via iOS Flaw
Security researchers warn that an iOS vulnerability lets malware scan iPhone photos and notes for crypto wallet recovery phrases.
KEY POINTS
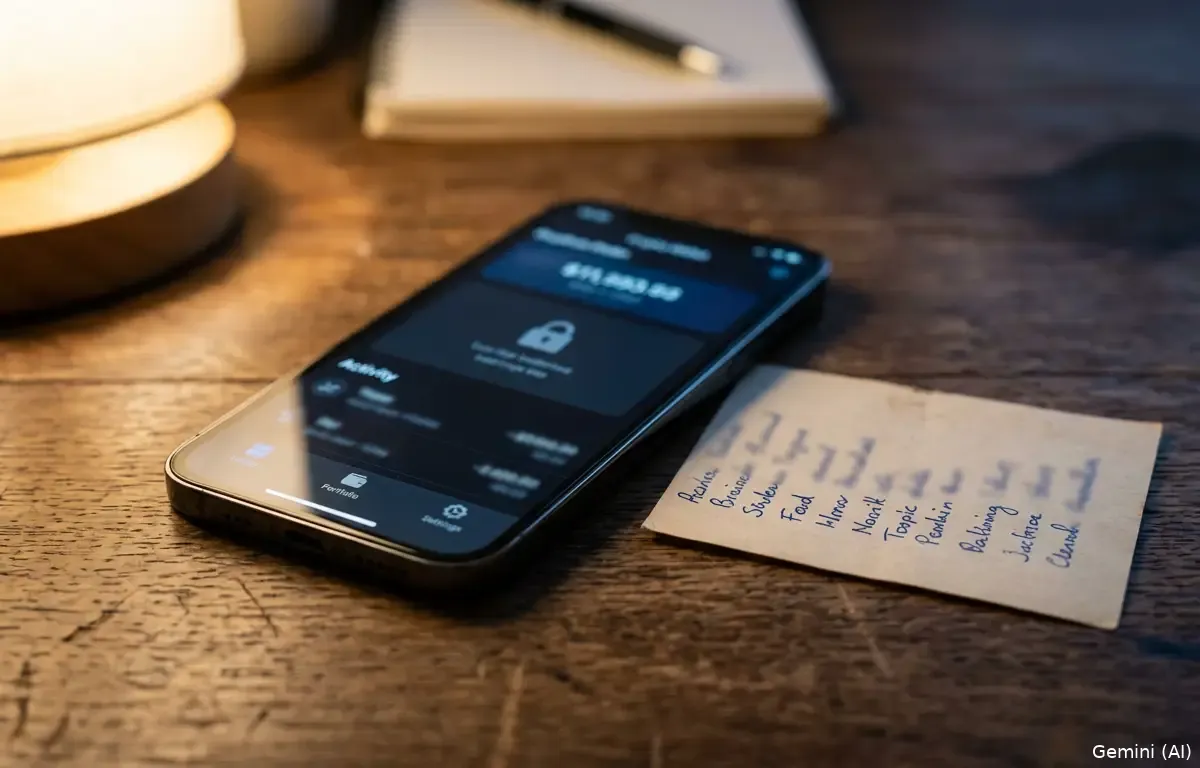
- DarkSword scans iPhone Photos and Notes for 12- or 24-word crypto seed phrases
- Eleven stolen recovery phrases were found on an attacker server
- Apple patched the exploited WebKit leaks in iOS 26.3
- Binance warns about the worse_query sandbox escape affecting iOS 26 and 27
- Censys found five servers distributing DarkSword in October
Security firm Censys discovered a hacking tool called DarkSword that targets iPhones to steal cryptocurrency wallet recovery phrases. The software scans the Photos and Notes apps for seed phrases consisting of 12 or 24 words. Researchers found eleven stolen recovery phrases on an attacker server, including wallets for TronLink, Bitget, Trust Wallet, Phantom, and imToken.
DarkSword exploits leaks in WebKit, the engine behind Safari and other iPhone browsers. Visiting an infected webpage is enough to infect a device, as long as the malicious tab remains open. The version examined by Censys used a Chinese-language lure page, and the kit is rented as a service to other criminals with a list of 75 customer accounts.
The tool includes separate modules for eighteen wallet applications, such as Coinbase, MetaMask, Exodus, and Uniswap. Apple patched all exploited vulnerabilities in iOS 26.3. Censys identified five servers still distributing the kit in October.
Separately, Binance warned Apple users about a dangerous iOS vulnerability called worse_query. The flaw allows malicious applications to access files normally isolated inside other apps, threatening seed phrases, private keys, and login credentials.
Binance says the issue affects iOS itself rather than its own wallet infrastructure. The vulnerability impacts iOS 26.7.1, 27.0.1, and 27.2, and researchers describe it as a sandbox escape affecting iOS 26 and iOS 27.
Users who suspect compromise should create new wallets on clean devices and move their funds. Binance also recommends resetting active login sessions and updating installed software. Censys could not determine who is behind DarkSword.
2 more sources below
COMMENTS (0)
No comments yet. Be the first.
RELATED STORIES

Turkey revokes electronic money licenses for two firms
The Central Bank of Turkey cancelled the operating licences of A Ödeme and Ozan Electronic Money, published in the Official Gazette on 11 November 2026.
Anthropic launches Claude Meetings, Sheets and Whiteboards to challenge Microsoft and Google
Anthropic adds AI meeting, spreadsheet and whiteboard tools to Claude ahead of its planned stock market listing.
Turkey issues NAVTEX for French cable research ship in Eastern Mediterranean
Turkey authorized French vessel Abeille Marengo to conduct marine research for the Greece-Cyprus power cable from November 10, 2026 to March 19, 2027.
- NASA Plans Permanent Moon Base with Nuclear Rover Launching in 2028
- Hot October CPI Report Raises Odds of December Fed Rate Hike
- Anthropic Withdraws $70-to-$80 IPO Price Range After Leak
- Teen Rescued After 521 Days in Oregon Basement Using Online Game
- Supreme Court Orders WhatsApp to Submit Digital Arrest Scam Measures
This page was compiled with AI assistance from the outlets named above and passed an automated language check before publication. Montegre has no reporters of its own; the byline names the outlets the story was compiled from. Method and editorial standards