Supply Chain Attack Hits 178 Major Websites Including BBC and Zoom
Malicious JavaScript injected through Optimizely stole crypto addresses and payment card details from visitors.
KEY POINTS
- 178 major organizations were affected through a compromised Optimizely platform
- Malware replaced crypto wallet addresses and stole payment card details
- Attackers targeted Bitcoin, Ethereum, Solana, TRON, and Litecoin networks
- Malicious code remained active for approximately 17 hours
- Researchers traced $7,040 in crypto to attacker-linked wallets
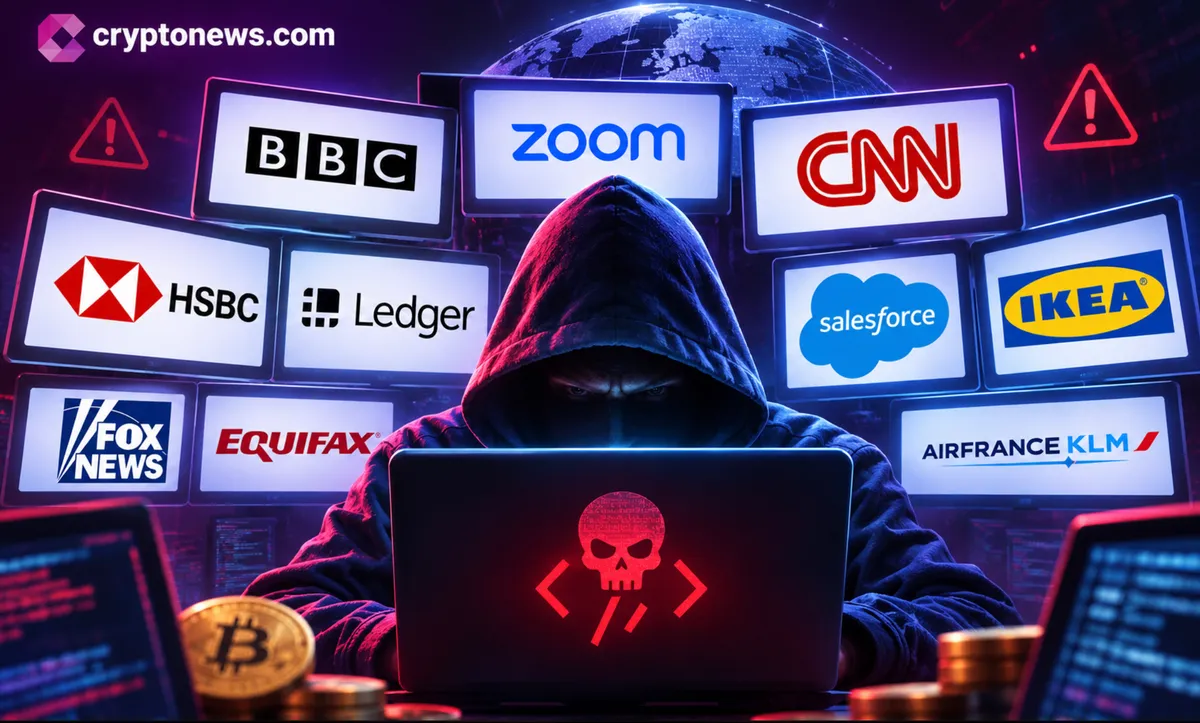
Hackers compromised Optimizely, a website experimentation platform used by major organizations including BBC, Zoom, CNN, HSBC, Salesforce, IKEA, and Ledger. Attackers injected malicious JavaScript into customer projects rather than breaking into each company’s servers individually.
The malware loaded automatically when visitors opened affected pages. It searched for cryptocurrency wallet addresses copied to the clipboard and replaced them with addresses controlled by attackers. It could also intercept copied addresses so users might paste fraudulent destinations elsewhere.
“Rather than breaking into every company’s servers individually, attackers injected malicious code into Optimizely customer projects.”
Payment card details and user data were also targeted, and iPhones and older iPads were hit with exploit kits. The attack affected Bitcoin, Ethereum, Solana, TRON, and Litecoin networks.
Report URI examined 1,611 Optimizely scripts and found 188 infected snippets belonging to 178 organizations. The first malicious code appeared in a BBC file on November 16 at 07:21 Turkey time. Attackers updated the software repeatedly throughout the day.
Cleanup began late at night. By 23:56 Turkey time, 169 files still contained malicious code, and by 00:52 on November 17 only one file remained affected. The sites carried malicious code for approximately 17 hours.
Security researchers identified $7,040 in crypto received by wallets linked to the campaign. Optimizely had not issued a statement about the incident at the time of reporting.
2 more sources below
COMMENTS (0)
No comments yet. Be the first.
RELATED STORIES
Recordings in singer Güllü death case sent to TÜBİTAK for analysis
Expert reports on security camera footage and audio recordings from the singer's fatal fall were forwarded to Turkey's scientific research council.
US and Nine Allies Sign San Francisco AI Supply Chain Declaration
The agreement aims to protect critical AI technologies and infrastructure from China amid rising tensions.
Lula Plans to Name First Ministers by Early December
President Luiz Inácio Lula da Silva aims to announce initial ministers for his fourth term before December.
- Milei Presents Growth Strategy to Business Leaders at CICyP Event
- Trustee Appointed to Sözcü TV, Chief Executive Detained
- Nvidia faces first earnings call without founder Jensen Huang
- Ghana commissions GEXIM-backed cashew factory in Techiman to boost exports and jobs
- California Sues OpenAI Over Uncontrolled AI Agents
This page was compiled with AI assistance from the outlets named above and passed an automated language check before publication. Montegre has no reporters of its own; the byline names the outlets the story was compiled from. Method and editorial standards